by super | Nov 4, 2025 | Elpro Technologies, Elpro Technologies Post
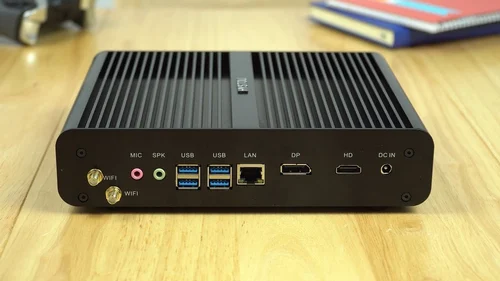
Every 39 seconds, another cyberattack hits. That statistic should make any business owner in India sit up and pay attention, especially if they are using Industrial Small PCs (ISPCs). These compact computers are changing how industries operate across the nation, boosting productivity and automating critical tasks in manufacturing, energy, transportation and healthcare. I have seen firsthand how these devices are becoming essential. Yet, this reliance creates a serious problem: keeping them safe from cyberattacks. When ISPCs connect to networks, they become easy targets for malicious actors. This can lead to operations grinding to a halt, data being stolen and significant financial hits. For Indian companies aiming for long term success, focusing on effective Industrial Small PC Cybersecurity India is not something to consider later. It is a necessity now.
The Cybersecurity Scene for ISPCs
ISPCs come with their own set of cybersecurity challenges, different from what you would see with regular desktop computers. They often operate in tough environments, rely on specific operating systems and software and connect to important infrastructure. Because of this, they need a security approach built just for them.
ISPC Vulnerabilities
Here is what makes ISPCs attractive targets for cyberattacks:
1. Limited Resources
ISPCs are built to be efficient and small. This means they often do not have a lot of processing power or memory. It can be hard to run comprehensive security solutions on them, like advanced antivirus software or complete intrusion detection systems. I have seen standard security suites slow down ISPCs significantly, impacting their main functions.
2. Older Systems and Software
Many industrial sites still use older systems and software that were not designed with cybersecurity as a priority. Upgrading these systems can be complicated and cause disruptions, creating vulnerabilities that can be exploited. I once worked with an industrial control system running on an extremely outdated operating system with well known security flaws. It was an easy target for attackers.
3. Specialized Tech
ISPCs often use specialized hardware and software made for specific industrial tasks. Finding compatible security tools can be difficult. I have had to create custom security solutions for some ISPC setups because there were no commercial options available.
4. Environmental Factors
ISPCs frequently operate in tough settings like factories, power plants and transportation hubs. They are exposed to extreme temperatures, humidity and electromagnetic interference. These conditions can damage the devices and make them more vulnerable to cyberattacks. I remember an incident where an ISPC in a dusty factory had a hardware failure, accidentally creating a backdoor for unauthorized access.
5. Lack of Security Awareness
If employees in industrial settings do not understand security best practices, it can lead to accidental security breaches. This could be from clicking on phishing links or using weak passwords. I have held training sessions to emphasize the importance of PC Security India and the possible results of careless actions.
Cybersecurity Recommendations for ISPCs in India
To protect ISPCs from cyberthreats, businesses should have a complete cybersecurity plan that addresses the unique challenges these devices present. Here are some key recommendations:
1. Risk Assessment and Vulnerability Management
Start with a complete risk assessment to find potential weaknesses and prioritize security measures. This assessment should cover everything in your ISPC environment, including hardware, software, network infrastructure and how you operate. I suggest using established frameworks like the NIST Cybersecurity Framework as a guide.
Vulnerability management means regularly scanning your ISPC network for known vulnerabilities and quickly applying patches. Use automated vulnerability scanning tools and manual security audits. I have consistently observed that proactive vulnerability management greatly reduces the attack surface of ISPC networks.
2. Network Segmentation and Access Control
Network segmentation means dividing your ISPC network into smaller, separate parts. This limits the damage from a security breach. This can be done using firewalls, virtual LANs and other network security technologies. I advise segmenting your ISPC network based on how critical each part is, separating critical systems from those less sensitive.
Access control means limiting who can access ISPCs and network resources based on the principle of least privilege. Give users only the minimum access they need to do their jobs. I use role based access control to manage user permissions and prevent unauthorized access to sensitive data and systems.
3. Device Protection and Intrusion Detection
Device protection means installing security software on ISPCs to protect against malware, viruses and other cyberthreats. This software should include antivirus scanning, intrusion detection and host based firewalls. I recommend choosing device protection solutions designed for environments with limited resources to minimize the impact on ISPC performance.
Intrusion detection systems watch network traffic for malicious activity and alert security personnel to suspicious events. These systems can be installed on ISPCs or at the network perimeter. I have implemented network based intrusion detection systems to watch traffic going to and from ISPC networks, adding an extra layer of security.
4. Secure Remote Access Protocols
Remote access to ISPCs is often needed for maintenance, troubleshooting and data collection. Insecure remote access introduces security risks. I secure remote access to ISPCs using virtual private networks (VPNs) with multi factor authentication (MFA). MFA requires users to verify their identity in multiple ways, like with a password and a one time code, before they can access the network.
5. Data Security and Backup Strategies
Data security transforms data into an unreadable format, protecting it from unauthorized access. I encrypt sensitive data stored on ISPCs and data sent over the network. Encryption keys should be stored securely and managed following industry best practices.
Regular data backups are important for disaster recovery and business continuity. I back up critical data from ISPCs to a secure, offsite location regularly. Backup data should be tested to make sure it is complete and can be recovered if data is lost.
6. Security Awareness Training
Security training is important for teaching employees about cybersecurity and how to protect ISPCs from cyberthreats. This training should cover topics like phishing awareness, password security and safe browsing habits. I hold regular security training sessions for employees who use ISPCs or access ISPC networks.
7. Incident Response Planning
Even with strong security measures, security incidents can still happen. That is why having a well defined incident response plan is important for guiding your response to a cyberattack. This plan should outline the steps to contain the incident, investigate what caused it and recover from the damage. I keep a detailed incident response plan that is regularly reviewed and updated to address the evolving threat landscape.
8. Physical Security Measures
While focusing on cybersecurity, do not forget physical security. ISPCs in remote or unsecured areas can be stolen or physically tampered with. I recommend implementing physical security measures like:
- Securing ISPCs in locked enclosures.
- Using cable locks to prevent theft.
- Installing surveillance cameras to watch ISPC locations.
- Restricting physical access to ISPC locations.
Considerations for Indian Businesses
Indian businesses must consider the specific cybersecurity rules and challenges within India. These include:
1. Following Indian Cybersecurity Regulations
The Indian government has created several cybersecurity regulations, like the Information Technology Act, 2000 and the National Cyber Security Policy, 2013, which businesses must follow. These regulations define the legal framework for cybersecurity in India and require businesses to protect their data and systems. I make sure my cybersecurity practices follow all relevant Indian cybersecurity regulations.
2. Addressing the Skills Shortage
India has a shortage of qualified cybersecurity professionals. This makes it difficult for businesses to find skilled people to implement and manage their cybersecurity programs. I invest in training and development programs to build cybersecurity skills within my organization.
3. Combating Cybercrime in India
India is a major target for cybercrime and experiences a high number of phishing attacks, malware infections and data breaches. Indian businesses must be especially watchful for these threats and implement strong security measures to protect themselves. I actively monitor the cyberthreat scene in India and adjust my security measures to match.
4. Government Initiatives
The Indian government has launched several initiatives to promote cybersecurity awareness and adoption, such as the Cyber Swachhta Kendra and the National Cyber Coordination Centre. Indian businesses can use these initiatives to strengthen their cybersecurity. I participate in government cybersecurity programs and share my knowledge with other organizations.
Embedded System Protection
ISPCs are often parts of larger embedded systems. These systems control critical processes across different industries and need specific security considerations. Securing these systems requires a complete strategy that goes beyond standard IT security measures.
1. Secure Boot Mechanisms
A secure boot process makes sure that only authorized software is loaded when the system starts up. This prevents malicious code from getting into the system before the operating system loads. I use secure boot mechanisms that verify the bootloader and operating system kernel are complete before execution.
2. Firmware Security
Firmware is the software embedded directly into the hardware and is a prime target for attackers. If compromised, attackers gain complete control over the device. I regularly update firmware to patch security vulnerabilities and use secure firmware update mechanisms to prevent malicious updates.
3. Hardware Security Modules (HSMs)
Hardware Security Modules (HSMs) are dedicated hardware devices that securely store and process cryptographic keys. These modules are designed to resist tampering and protect sensitive data from unauthorized access. I use HSMs to store encryption keys and other sensitive data used by ISPCs.
4. Real Time Operating System (RTOS) Security
Many ISPCs rely on Real Time Operating Systems (RTOSs) for their predictable behavior. Securing these RTOSs is critical because vulnerabilities can have immediate and severe consequences. I select RTOSs with built in security features and regularly patch them to address security vulnerabilities.
5. Input Validation and Output Sanitization
Embedded systems often interact with external devices and networks. Input validation and output sanitization are important to prevent malicious data from entering the system or sensitive data from being leaked. I implement strict input validation and output sanitization routines to protect ISPCs from these attacks.
Threat Intelligence
Effective cybersecurity requires staying ahead of the evolving threat landscape. Threat intelligence is important for proactively identifying and mitigating potential threats to Compact Computer Network Security.
1. Threat Monitoring and Analysis
Threat monitoring means continuously watching network traffic and system logs for suspicious activity. This can be done using Security Information and Event Management (SIEM) systems and other security monitoring tools. I analyze threat data to find patterns and trends that help me anticipate and prevent future attacks.
2. Threat Intelligence Feeds
Threat intelligence feeds provide information about known cyberthreats, like malware signatures, IP addresses of malicious servers and phishing domains. I subscribe to threat intelligence feeds from reputable sources and integrate them into my security monitoring systems.
3. Vulnerability Research
Vulnerability research means actively searching for new vulnerabilities in ISPC hardware and software. This can be done through penetration testing, code reviews and working with security researchers. I conduct regular vulnerability assessments to find and fix potential security flaws.
4. Incident Response Drills
Incident response exercises simulate real cyberattacks to test how well your incident response plan works. These exercises help find weaknesses in your plan and improve the readiness of your security team. I conduct regular incident response drills to make sure I am prepared to respond to a cyberattack.
5. Information Sharing
Collaboration and information sharing are essential for effective cybersecurity. I collaborate with other organizations, like industry groups and government agencies, to share threat intelligence and best practices. This helps me stay ahead of the evolving threat landscape and improve my security.
The Future of Industrial Small PC Cybersecurity in India
The future of Industrial Small PC Cybersecurity India will likely be shaped by key trends:
1. Automation and Artificial Intelligence (AI)
Automation and artificial intelligence will become more important in cybersecurity, automating tasks like threat detection, vulnerability management and incident response. AI powered security solutions can analyze large amounts of data to find patterns and anomalies that would be difficult for humans to detect. I am looking at using AI powered security solutions to improve my cybersecurity.
2. Cloud Based Security Solutions
Cloud based security solutions offer advantages over traditional on premise solutions, like scalability, cost effectiveness and ease of use. I am moving some of my security services to the cloud to take advantage of these benefits.
3. Zero Trust Security Architecture
Zero Trust is a security model that assumes that no user or device is inherently trustworthy, regardless of their location. This model requires all users and devices to be authenticated and authorized before being granted access to resources. I am adopting a Zero Trust security architecture to strengthen my security.
4. Regulatory Compliance
The Indian government will likely introduce stricter cybersecurity regulations soon. Businesses need to be ready to follow these regulations and invest in cybersecurity programs that meet the standards. I am closely watching the regulatory environment and adjusting my security practices accordingly.
5. Cybersecurity Skills Development
Addressing the cybersecurity skills shortage will be critical for ensuring the security of ISPC networks in India. I am investing in cybersecurity training and development programs to build a skilled workforce capable of protecting critical infrastructure.
Securing industrial small PC networks in India is complex and ongoing. Indian businesses can protect their critical infrastructure and maintain their operational success by implementing the recommendations above and staying informed about the evolving threat scene. The key is to use a layered defense approach, combining technical controls with policies and employee training. By working together, we can create a more secure industrial environment in India.